Out-of-context alerts
A physical firewall flagged as critical for a fully remote, cloud-only company. When most alerts don’t apply, the team stops looking.
Adaptive GRC
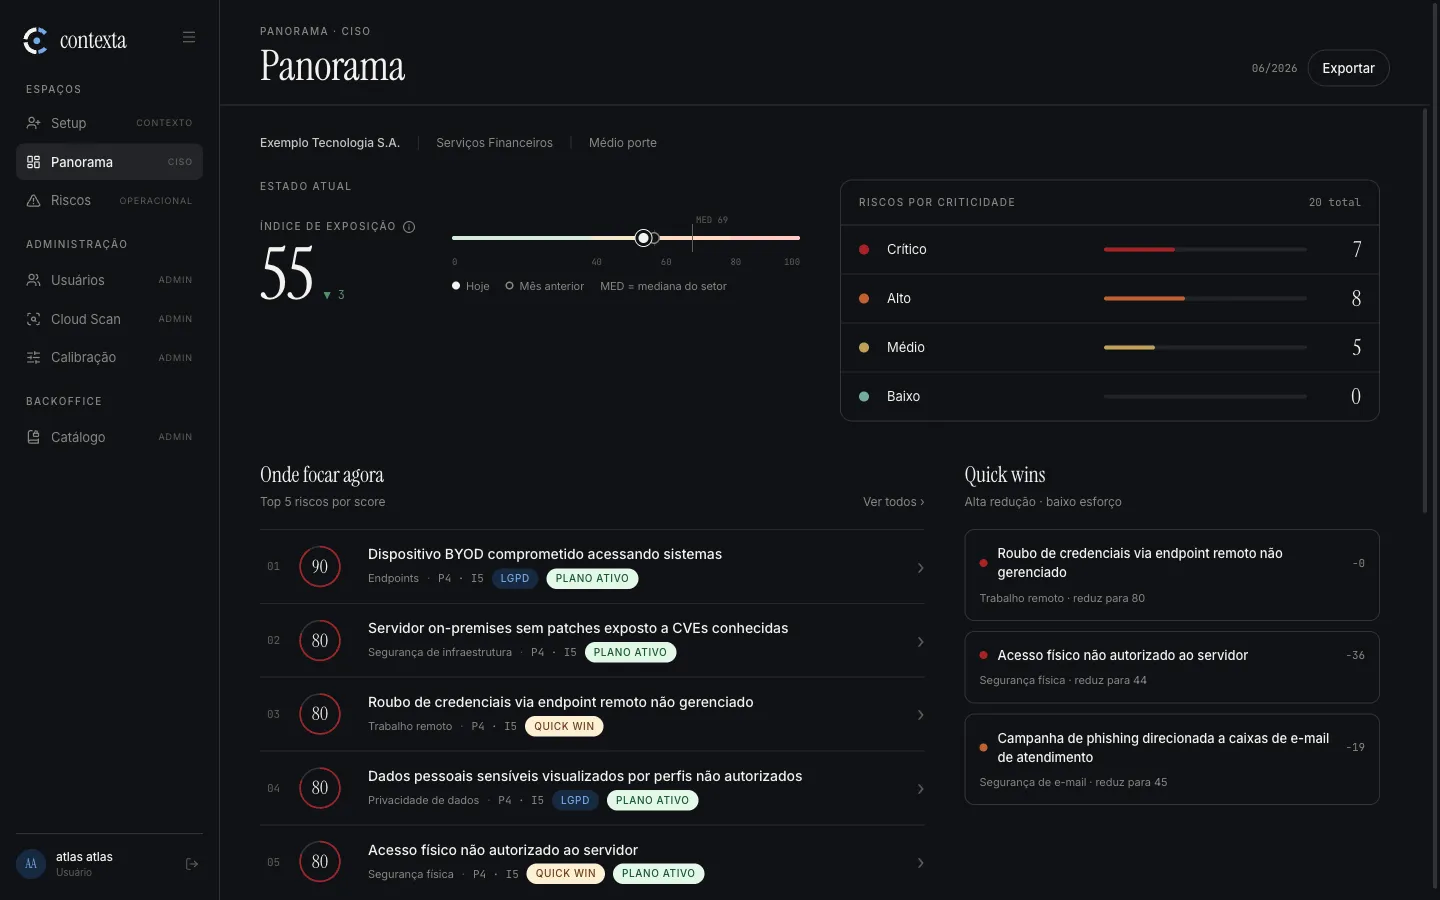
Contexta prioritizes risks, scores and controls based on how your company actually operates: size, industry, work model, the data you handle and what is exposed to the internet.
The problem
A physical firewall flagged as critical for a fully remote, cloud-only company. When most alerts don’t apply, the team stops looking.
Hours spent fixing whatever has high technical severity while the risks that hurt your business, like personal data and public APIs, wait in line.
A list of vulnerabilities doesn’t answer the board’s question: how much could this cost, and where should we invest first?
How it works
Size, industry, work model, data handled, external exposure and the frameworks you need to meet.
The risk catalog is filtered and adjusted to your profile. What doesn’t apply gets out of the way, what matters rises.
Every score shows where it came from: baseline, context adjustments and applied mitigation.
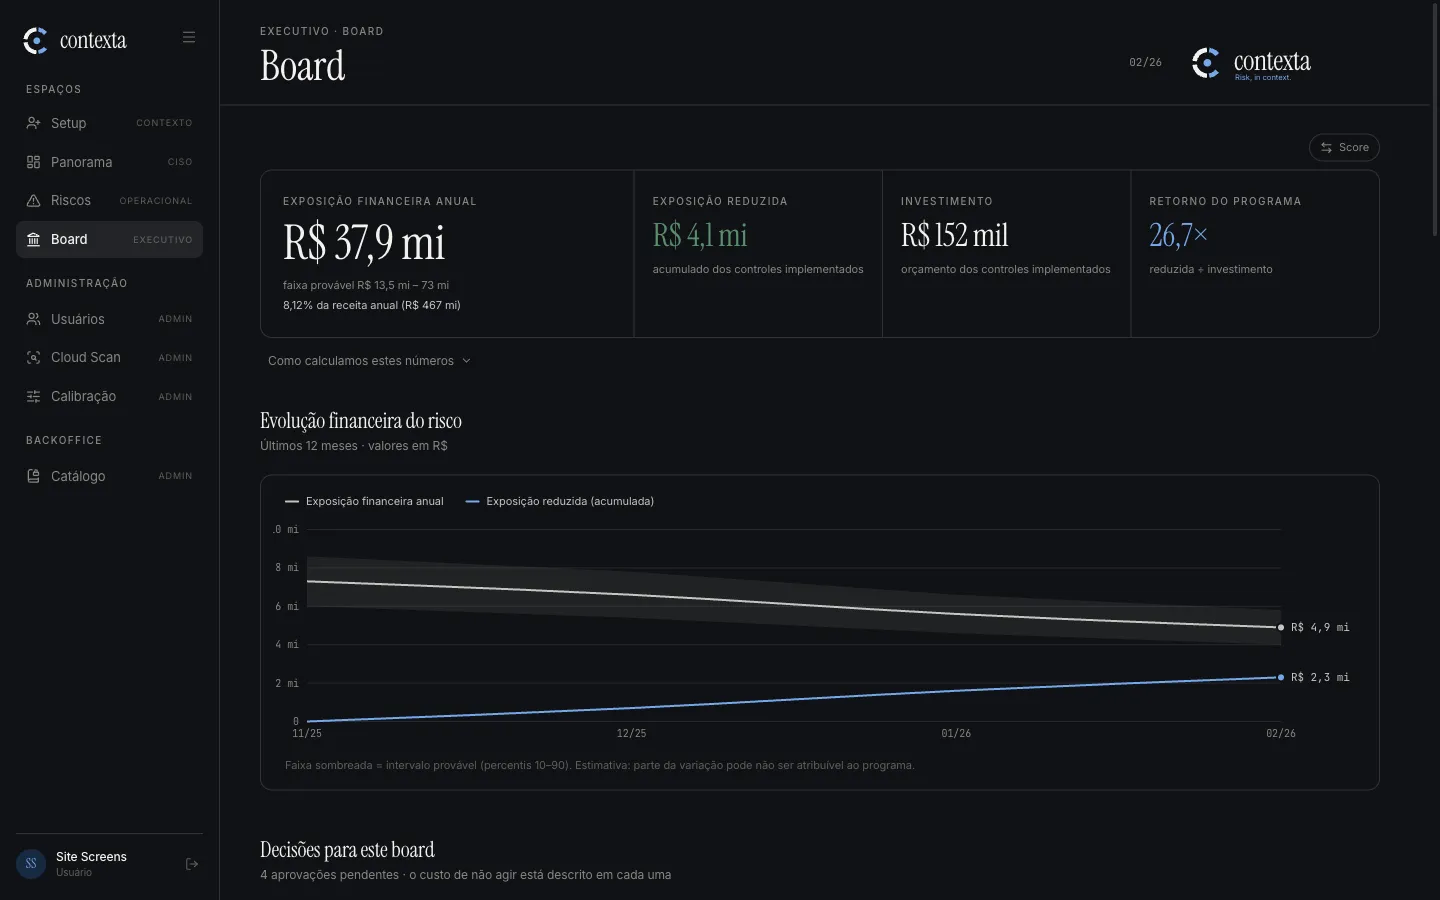
A treatment plan with cost and risk reduction, and an executive board that translates exposure into money.
Executive board
Expected annual loss with a likely range, the decisions waiting on the board and the return of each treatment, in the language of whoever approves the budget.
From risk to plan
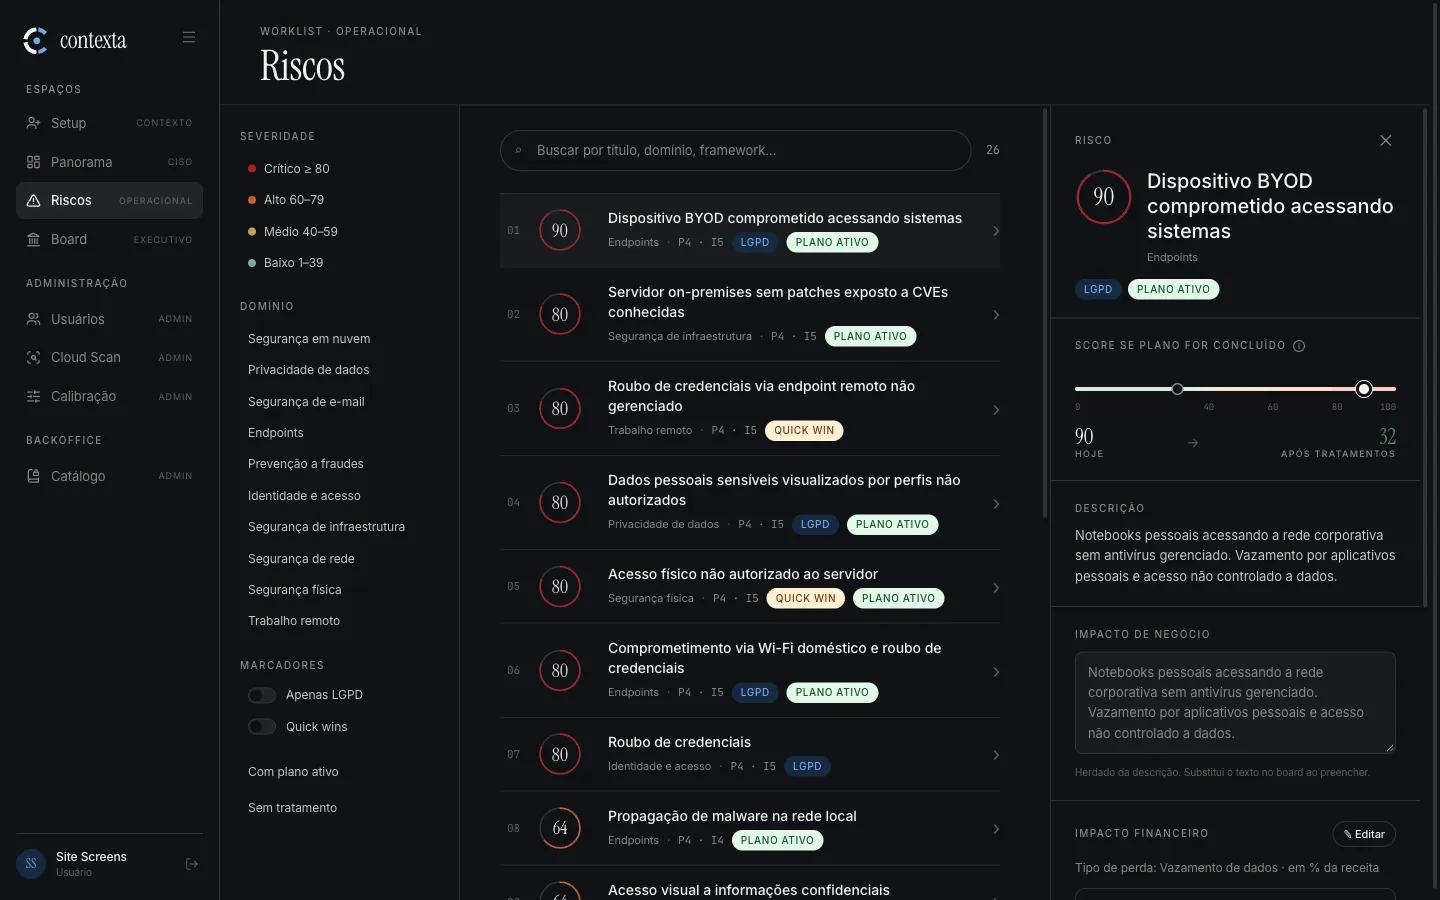
Every risk shows its current score, the expected score after the treatment plan and the impact on the business and in money. Controls in your AWS and GCP accounts are validated automatically.
Who it’s for
CISOs and security owners who need to prioritize with a small team and defend the investment to the board.
SaaS, fintech, e-commerce and healthtech, where personal data, APIs and cloud concentrate the real risk.
Teams that must meet LGPD, ISO 27001 or SOC 2 and want to know what actually reduces exposure.
A 30-minute call to show the product and understand your company’s context.